
Are your company data really safe?
When we think about the security of our company data, our minds immediately go to internal defenses: do we have a good firewall? Is the antivirus up to date? Are the office servers protected? This approach, as fundamental as it is, risks showing you only half the problem today. In fact, in the current digital landscape, an enormous amount of sensitive information, credentials, and access permissions passes through and settles every day well beyond the walls of your company, often ending up in cybercrime underground markets without anyone noticing. The truth is that companies are no longer vulnerable only because of what happens within their systems, but because of everything that is already freely accessible online to any malicious actor.
“Our Cyber Risk Investigation service verifies whether your corporate data or credentials are exposed on the dark web, present in stolen databases, or involved in data breaches and cyber theft through non-invasive analysis that has absolutely no impact on your company’s systems.”
The corporate perimeter paradox
In today’s digital landscape, we are used to thinking of cybersecurity as a matter of domestic walls: protecting the office, securing internal servers, installing antivirus software on employees’ PCs. The reality, unfortunately, is that an enormous amount of company data passes through, scatters, and settles every day well beyond the corporate perimeter. This information often ends up in the wrong hands without anyone in the company noticing, becoming the perfect foundation upon which cybercriminals build their attacks. In practice, companies are vulnerable not only because of what happens inside their systems, but because of what is already freely available online.
Staying ahead of the game with non-invasive intelligence
Instead of waiting for a hacker to decide to exploit this information to leverage your business, today it is possible to stay ahead of the game. This is where Cyber Risk Investigation comes in—an advanced intelligence activity that analyzes data circulating on the web, deep web, and dark web linked to your company’s domain. The real strength of this approach is its entirely non-invasive nature.
Information gathering is conducted entirely from the outside, meaning there is no need to install invasive software, run intrusive tests on your network, or, worse yet, disrupt the daily operations of your IT systems.
The illusion of security and the human factor
The paradox of modern security is that you can spend tens of thousands of euros to secure your internal network, but you will still remain vulnerable if your purchasing manager uses their corporate email and the exact same password as the control panel to register on a news site or a third-party e-commerce platform that is subsequently breached. When that site suffers a data leak, your company’s credentials go straight to cybercrime underground markets, ready to be tested against your real systems.
What we look for beneath the surface of the web
During this investigation, we scour the network looking for those critical elements that attackers typically use as an entry point. We hunt for compromised credentials on the dark web, such as corporate emails and passwords stolen from employees through breaches of third-party sites where they had registered. We look for exfiltrated tokens and session cookies, which could allow a malicious actor to directly access systems, bypassing traditional passwords.
We then analyze the web perimeter using OSINT techniques, identifying exposed URLs, misconfigured servers, visible databases, and sensitive JSON files.
Finally, we verify the presence of typosquatting threats, meaning counterfeit domains very similar to the corporate one, registered by third parties with the sole purpose of launching targeted phishing campaigns against your clients or your partners.
Measuring danger with the Cyber Risk Index
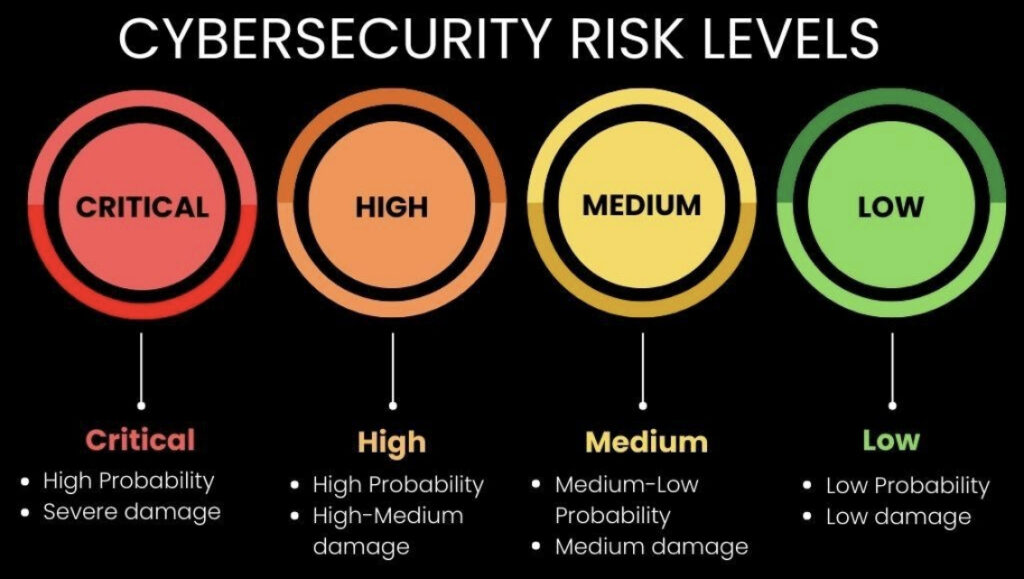
At the end of this analysis, you won’t be left with just a simple list of incomprehensible raw data, but with a clear, immediate, and actionable metric: the Cyber Risk Index.
This index quantifies your company’s actual risk level based on the number of exposed services, the severity of the identified leaks, and the volume of sensitive information already accessible to anyone.
Monitoring this index over time is the best way to understand whether your defenses are improving and where budget allocation needs to be prioritized.
Legal protection, GDPR, and business continuity
Conoscere questo indice non è solo un esercizio di prudenza tecnica, ma una vera e ferrea tutela legale ed economica per il tuo business. Nel momento in cui i dati aziendali o le sessioni dei clienti fluttuano nel Dark Web, il rischio di un data breach imminente è altissimo, con tutto ciò che ne consegue in termini di sanzioni GDPR, blocco totale dell’operatività e, soprattutto, distruzione della reputazione del tuo brand agli occhi dei clienti.
Giocare d’anticipo con un’investigazione predittiva significa poter dimostrare alle autorità e ai partner che l’azienda si muove attivamente per proteggere le informazioni prima che il danno si manifesti.
From discovery to defense strategy
Identifying the flaws, however, is only half the job. The service provides a strategic guide to neutralize the emerged risks. If we discover compromised credentials, we guide you through a timely password change and the implementation of cybersecurity awareness training for your team. If exposed files or servers emerge, we help you correct misconfigurations and optimize access management. If, on the other hand, the critical issues concern the network infrastructure, we can launch targeted deep dives through an Extended Vulnerability Assessment to thoroughly test the solidity of your public IPs.
CMV Group’s predictive approach
In today’s context, waiting for an attack to occur and then scrambling to fix the damage leads to devastating financial, legal, and reputational costs. Choosing predictive cybersecurity means flipping this paradigm entirely: it means having the exact insights needed to act ahead of time, eliminating weak points before an attacker can find them.
At CMV Group, we spend our days designing solid software architectures and managing sensitive cloud infrastructures. We know exactly how an attacker thinks because we understand the critical vulnerabilities of a production system firsthand. This is why our Cyber Risk Investigation doesn’t just hand you an automated report generated by impersonal software, but rather a critical, expert analysis interpreted by code professionals, ready to be transformed into a concrete defense strategy.
If you want to discover what the web really knows about your company and find out your Cyber Risk Index, contact us today to request a Cyber Risk Investigation session.
Did you find this article useful? Share it with the person in charge of security and privacy at your company. .